FYEO Security Scanner logo

    FYEO Security Scanner

    AI security scanning for smart contracts, trained on 300+ real audits.

    Built on FYEO's own security reasoning model. It reasons through smart contracts, APIs, integrations and dependencies like a senior auditor, helping catch flaws unique to your code—not just patterns from known bugs. Run PR, third-party dependency and full audits.

    Your code is never stored after a scan.

    scanner.fyeo.io
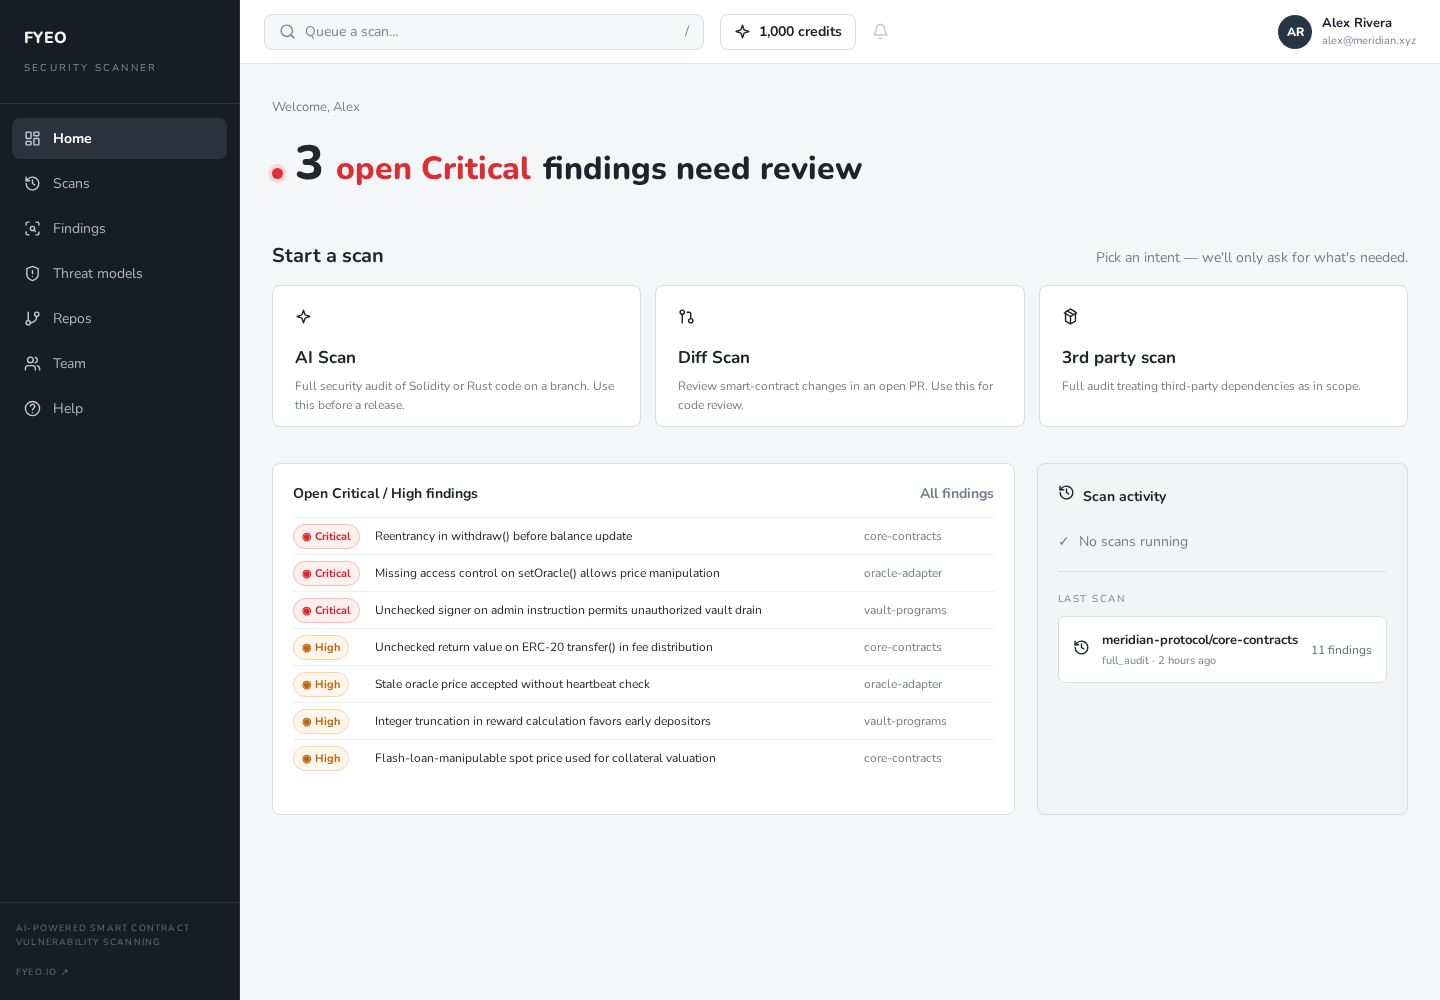
    FYEO Security Scanner dashboard showing scan options and open findings

    A finding, end to end

    What a finding looks like.

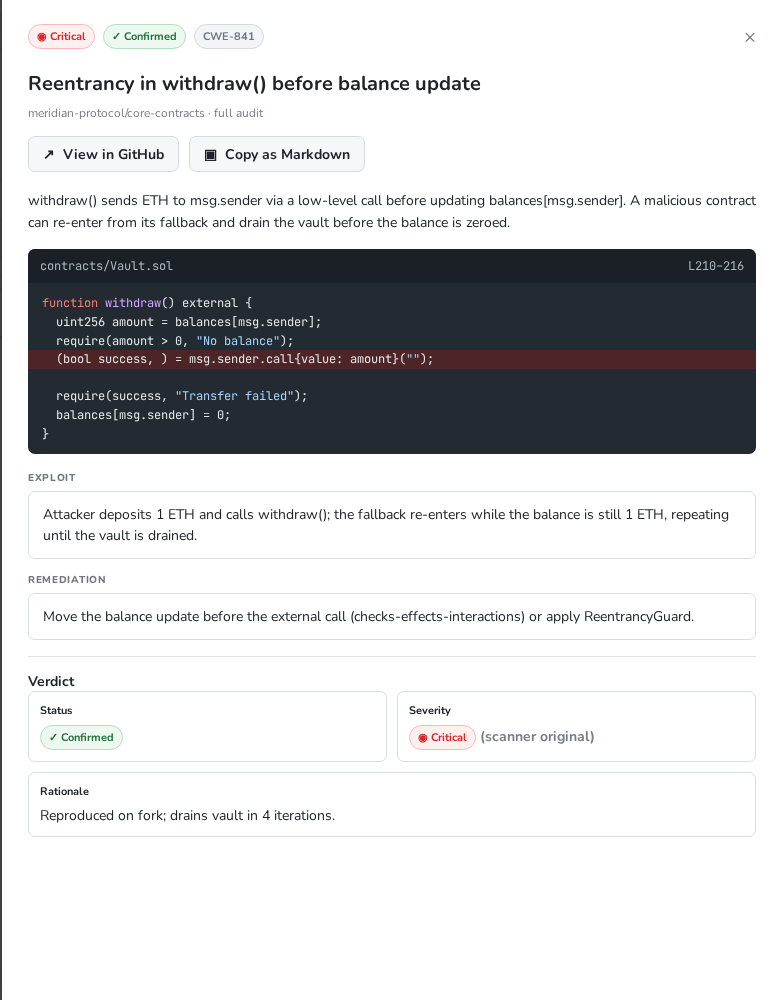
    Every result is structured for a security review: evidence, exploitability, remediation, and an auditable verdict in one place.

    1. 1Ranked by severity, mapped to CWE
    2. 2Exact file and line, vulnerable code highlighted
    3. 3Plain-language exploit path and fix
    4. 4Confirmed by a FYEO auditor when it matters
    FYEO Security Scanner finding with severity, vulnerable code, exploit path, remediation, and auditor verdict

    How it works

    From repository to reviewed finding.

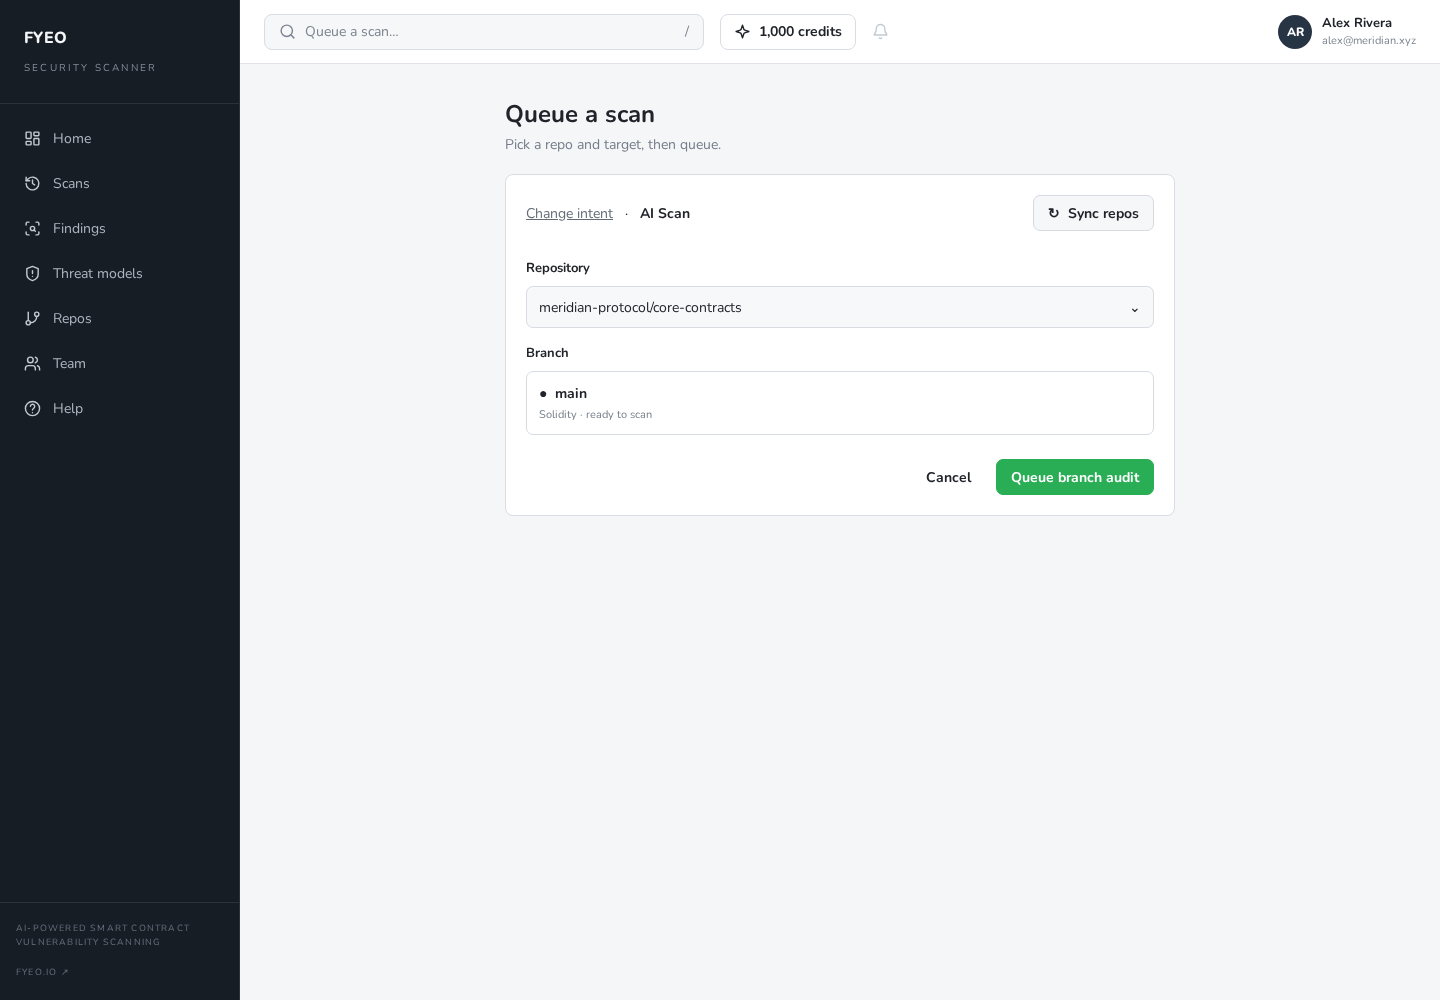
    1. FYEO Security Scanner repository and branch selection screen
      01

      Connect a repo

      Choose exactly which repository FYEO can access through GitHub.

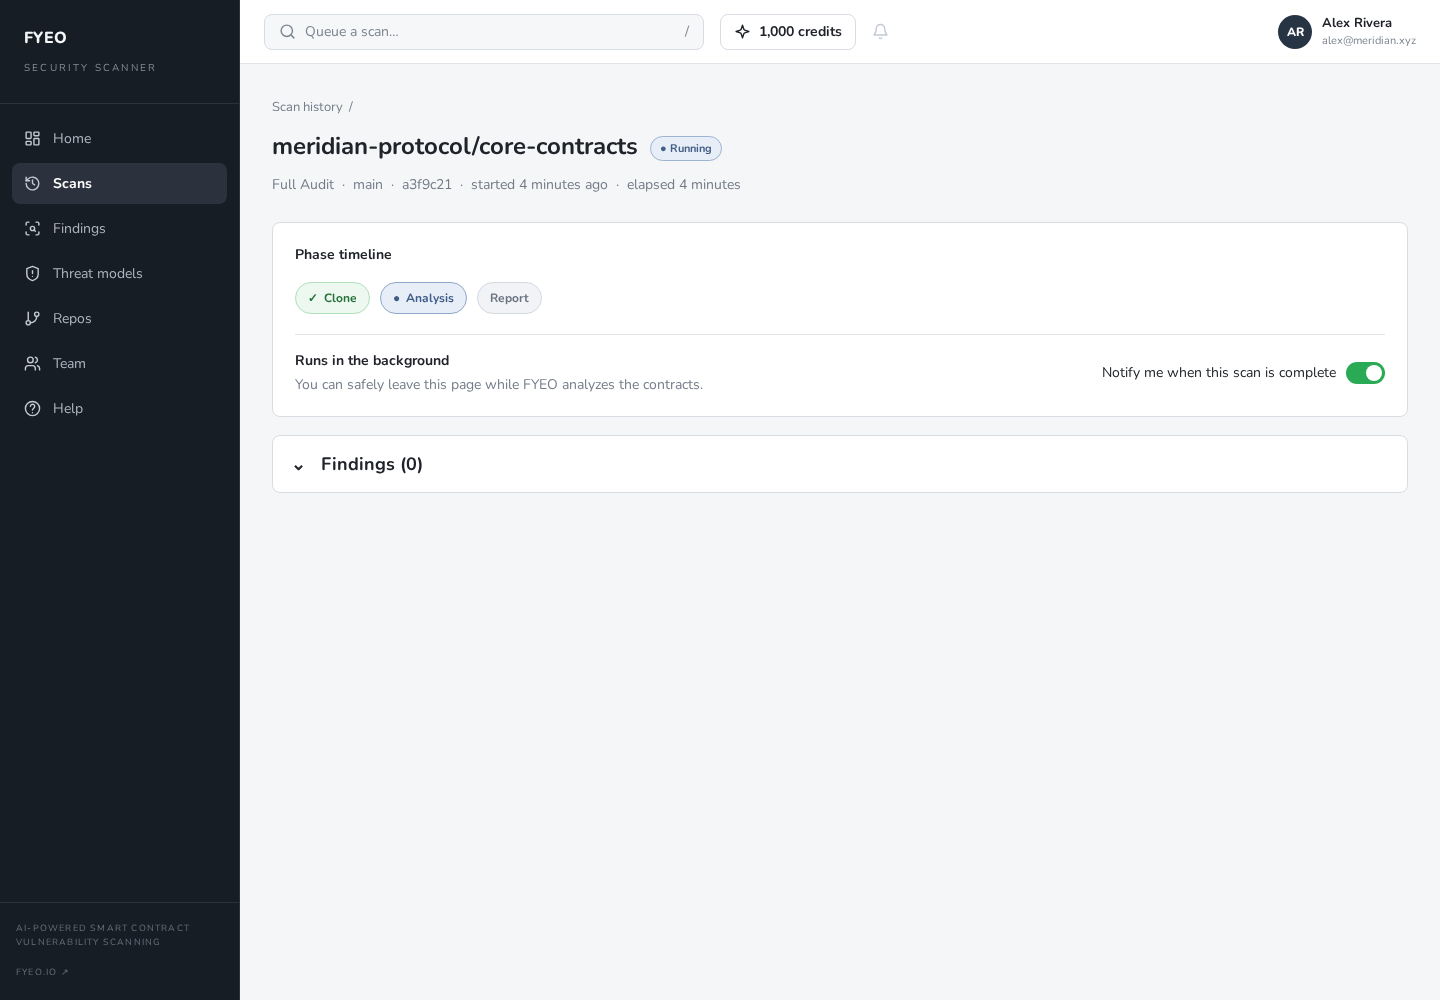
    2. FYEO Security Scanner showing a full audit running in the background
      02

      Scan

      Run a full or diff audit in the background while your team keeps working.

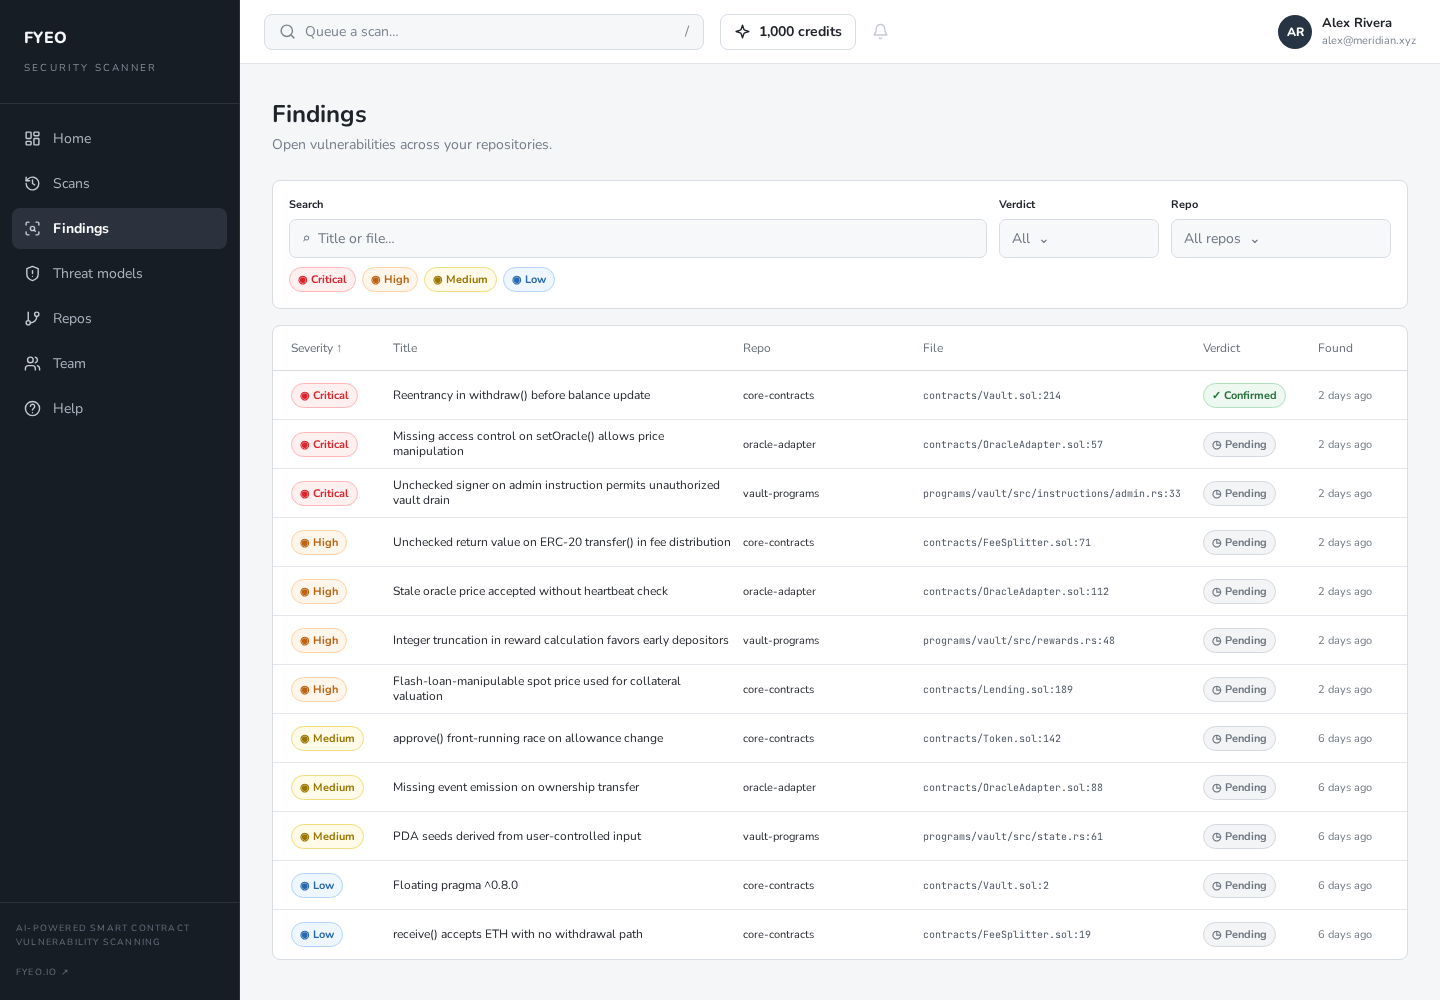
    3. FYEO Security Scanner findings list ranked by severity
      03

      Triage

      Review severity-ranked findings and escalate anything ambiguous to a human auditor.

    Purpose-built and private

    AI grounded in how auditors work.

    The Scanner combines specialist models, FYEO audit experience, and strict source-code handling in one review workflow.

    Built from real audit work

    Proprietary models trained on 300+ audits, with a reinforcement-learning feedback loop from FYEO security engineers.
    Fine-tuned for vulnerability classes

    Purpose-built models run 10–20× faster than untrained cloud-based alternatives, with no per-token cost ceiling.

    Self-hosted inference

    Your code runs on FYEO infrastructure.

    Least-privilege repository access

    Grant access per repository. Source is processed for the scan and never stored afterward.

    Flexible credit pricing

    Pay for the scanning you need.

    Start with 50 free credits. Pick a monthly plan, or buy credits as you go — no plan required.

    Exact price shown before every scan

    Failed scans refunded automatically

    Start free

    Free

    $0

    50 credits at signup, valid 30 days

    A full audit of a small project plus a couple of PR reviews — no card required.

    • 50 credits at signupValid 30 days
    • No credit card required
    • Unlimited repositories
    • 1 seat (owner)
    Start free

    50 signup credits are valid for 30 days.

    New

    Dev

    $59/mo

    40 credits / month

    For a solo dev keeping one small project continuously covered.

    • 40 credits / monthCredits pay for scans — no repo limits
    • Unlimited repositories
    • 1 seat (owner)
    • Findings history & trends
    • Standard support
    Choose Dev

    Auto-renews monthly at $59/month until you cancel. Cancel anytime in Billing. Terms.

    Starter

    $99/mo

    80 credits / month

    One actively developed project.

    • 80 credits / monthCredits pay for scans — no repo limits
    • Continuous scanning on every PR
    • Unlimited repositories
    • 1 seat (owner)
    • Findings history & trends
    • Standard support
    Choose Starter

    Auto-renews monthly at $99/month until you cancel. Cancel anytime in Billing. Terms.

    Most Popular

    Growth

    $300/mo

    280 credits / month

    A team shipping across several repos.

    • Everything in Starter, plus
    • 280 credits / monthScan every project your team ships
    • Team seatsUp to 5 team seats
    • Findings history & trends across repos
    • Standard support
    Choose Growth

    Auto-renews monthly at $300/month until you cancel. Cancel anytime in Billing. Terms.

    Pro

    $1,500/mo

    1,600 credits / month

    Heavy continuous scanning plus human auditor hours.

    • Everything in Growth, plus
    • 1,600 credits / monthContinuous coverage at scale
    • Human expert audit includedReal auditors review your code, not just AI
    • Up to 10 team seats
    • 4 Senior Auditor hours / mo
    • Fix verification by auditors
    • Priority scanning queue
    • Priority support
    Choose Pro

    Auto-renews monthly at $1,500/month until you cancel. Cancel anytime in Billing. Terms.

    Pay as you go

    Top-up credits, no subscription

    Buy a one-time credit pack whenever you need one.

    40 credits$59
    160 credits$199
    800 credits$899

    Enterprise

    For larger orgs and regulated environments.

    • Everything in Pro, plus
    • Unlimited team seats
    • SLA + escalation paths
    • Custom credit allotment
    • Multiple protocols / orgs
    • Dedicated security contact
    Contact sales

    Security Scanner FAQ

    How do I check if my vibe-coded app or smart contract is secure?
    Connect your GitHub repository to FYEO Security Scanner and run a full audit, then review the severity-ranked findings and fixes. Use PR audits for each change and dependency audits for third-party libraries. Automated scanning helps find vulnerabilities; it is not a guarantee of security, and high-stakes releases benefit from human review.
    Is there an AI security scanner that works with Claude or ChatGPT?
    Yes. FYEO Security Scanner connects to Claude, ChatGPT and other MCP clients through its MCP server. Connect your FYEO account to read scan results and request estimates. Queueing scans is off by default: enable AI apps access in your account and approve the quoted price before a scan is queued. See fyeo.io/mcp for setup.
    How much does a security scan cost?
    New FYEO Security Scanner accounts get 50 free credits, no card required. Scan costs depend on the scan type and repository size. You see the exact credit price before every scan, and failed scans are refunded automatically. Monthly plans start at $59; one-time top-up packs are also available. See fyeo.io/pricing for the current plans.
    How is FYEO different from using a general coding model to find bugs?
    FYEO is built on its own security reasoning model. It reasons through code like a senior auditor rather than relying only on patterns from known bugs, helping identify flaws unique to your code. Its review workflow produces severity-ranked findings with evidence, exploit paths and remediation for smart contracts, APIs, integrations and dependencies.

    Scan your first repo free.

    Sign in with GitHub and get expert-grade findings in minutes.

    Start free — 50 credits, no card required