FYEO Blog
Security insights, audit reports, and industry analysis from our experts.
Supply Chain Attacks Weaponize Web3 as C2 for Cloud Credentials
Hackers are increasingly using public blockchains as resilient command-and-control (C2) channels for supply chain malware, targeting cloud credentials. Learn how this new Web3 attack vector works and what you can do to protect your systems.
Bitget's $387.5M Zero-Day Supply Chain Attack
Bitget's $387.5 million loss highlights critical zero-day vulnerabilities in third-party security products and the escalating supply chain risks in Web3 infrastructure. Learn how to protect your protocol from such advanced threats.
Haruko Hack: Supply Chain Attack Hits 15 Crypto Firms
A targeted supply chain attack on crypto infrastructure provider Haruko exposed client API keys and trading data, leading to fund losses. Learn more.
Data Breach Alert: Revolut and Swiss Bitcoin Pay Expose Customer Data
A recent wave of data breaches at Revolut and Swiss Bitcoin Pay highlights the critical importance of robust information security in Web3. Learn how these incidents unfolded and what they mean for user privacy and platform security.
Web3 Security Shifts: Infrastructure Failures & Operational Risks
A new report from Blockaid highlights a critical shift in Web3 attacks: 74% of losses now stem from infrastructure failures, not just smart contract bugs. Learn how to protect your protocol.
Liquid Network Hack: $320M BTC-Based Funds Drained
The Bitcoin-based Liquid Network was breached, resulting in a $320 million loss from its federation wallet. Understand the implications and how FYEO enhances blockchain security. Read more.
Sui Full Sail Drained by Switchboard Oracle Compromise
Full Sail, a DeFi protocol on Sui, shut down after a $91,000 exploit linked to the Switchboard oracle. Learn about oracle security and DeFi risks. Read more.
AI-Enhanced Voice Phishing: The Wall Street Cyber War
Wall Street hedge funds are under attack from AI-enhanced voice phishing (vishing), impersonating staff to steal credentials. Learn about this new threat and how to defend against advanced AI cyberattacks.
Coldcard Firmware Flaw: $89M Bitcoin Hardware Wallet Exploit
A critical Coldcard firmware flaw led to an $89 million Bitcoin hardware wallet exploit. Discover how this 2021 bug was leveraged and what it means for hardware wallet security. Read more.
Verus Bridge Under Siege: $20M Lost in Double Exploit
The Verus Bridge suffered two distinct attacks, resulting in a staggering $20 million loss. This dual exploit highlights critical vulnerabilities in cross-chain bridge security, urging a closer look at DeFi protection measures. Learn how FYEO can help secure your assets.
North Korean Hacker Infiltration: Consensys and Web3 Supply Chain Risk
A major blockchain firm, Consensys, reportedly hired a North Korean hacker, highlighting the escalating supply chain risks in Web3. Learn how to protect your protocol.
Unpacking the $972M Crypto Loss in H1 2026: A Deeper Look
Despite a 57% drop in monetary losses, crypto hacks reached a record number in H1 2026. Discover the new security threats and how to protect your Web3 assets.
Crypto Hacks on the Rise: 207 Incidents in H1 2026
New data reveals a record 207 crypto hack incidents in H1 2026, highlighting escalating Web3 security threats. Learn how to protect your DeFi protocol. Read more.
Polymarket Phishing Puts Prediction Markets at Risk
A $3.1 million phishing attack on Polymarket highlights critical Web3 frontend vulnerabilities. Learn how to secure your assets and prevent future exploits. Read more.
U.S.-Iran Cyber Escalation: The Digital Geopolitical Threat
A deep dive into the recent U.S.-Iran cyber incidents and their implications for Web3 security. Understand the digital battleground and protect your assets.
Social Engineering: Web3's Most Underrated Threat
Social engineering attacks are rapidly becoming Web3's most costly threat, often bypassing technical security. Learn how to protect against these sophisticated scams.
Q2 2026: DeFi Hacks Surge to All-Time High
Q2 2026 marked a record quarter for DeFi hacks, with over 70 exploits causing $746 million in losses. Unpack the surge in this critical report.
Web3 Financial Security: Stablecoin Infrastructure Under Attack
Stablecoin infrastructure experienced over $328 million in losses due to bridge incidents, with wallet compromises exceeding code vulnerabilities. Read more.
Morse Code Prompt Injection: How an Attacker Tricked Grok and Bankrbot Out of $200K
A threat actor smuggled a malicious command past Grok's safety filters by encoding it in Morse code, then used Grok to relay the decoded instruction to Bankrbot — moving 3 billion DRB tokens in a single transaction.
DeFi Requires Error Correction, Operational Security Is Key
Dive into why robust error correction mechanisms and stringent operational security are paramount for DeFi protocols. Learn how to protect your assets with FYEO.
Smart Contract Vulnerabilities: Preventing DeFi Fraud
Smart contract vulnerabilities are a leading cause of DeFi fraud. Learn how robust audits and proactive security measures can prevent significant losses.
AI Zero-Day Exploit: Google Warns of Advanced AI Cyberattacks
Google reveals the first AI-generated zero-day exploit, signaling a new era of sophisticated cyber threats. Learn how AI is weaponizing attacks against crypto and other industries.
AI in Web3 Security: The New Exploit Landscape
Artificial Intelligence is rapidly reshaping Web3 security, acting as both a potent weapon for attackers and a crucial shield for defenders. Learn more.
Polkadot Bridge Exploit: 1 Billion Tokens Minted & Security Risks
A recent Polkadot bridge exploit allowed attackers to mint 1 billion tokens, highlighting critical vulnerabilities in cross-chain interoperability. Read more about its impact and prevention.
North Korean Hackers Exploit DeFi: $577M Stolen
North Korean state-sponsored hackers stole $577 million in early 2026, primarily targeting DeFi protocols like Drift Protocol. Learn how to protect your Web3 assets.
Syndicate Labs Bridge Attack: Private Key Leak Exposes Cross-Chain Risks
A private key leak at Syndicate Labs led to a nearly $18.5 million SYND token theft via a malicious cross-chain bridge upgrade. Learn about this critical cross-chain vulnerability and how FYEO enhances blockchain security.
April 2026: The Most Hacked Month in Crypto History
April 2026 set a grim record: ~30 incidents and over $625M stolen. Private key compromises and multi-sig phishing now drive most DeFi losses — here's what to do.
Crypto Private Key Breaches: Emerging Web3 Security Threat
Recent crypto attacks show a concerning shift from smart contract exploits to private key breaches and access control issues. Understand this emerging Web3 security threat and how to protect your assets by reading more.
ZetaChain GatewayEVM Exploit: Cross-Chain Security Risks
A recent vulnerability in ZetaChain's GatewayEVM contract led to a mainnet pause, highlighting critical cross-chain security risks. Understand the exploit and protect your protocols.
North Korean Hackers: Top Threat to Crypto Security
North Korean state-sponsored hacking groups have emerged as the dominant threat to Web3 security, stealing over $500 million in a single month. Learn how to protect your assets.
Vercel Breach: Supply Chain Attack on Frontend Cloud
Vercel, a leading frontend cloud platform, recently suffered a significant security breach. Learn how this supply chain attack unfolded and its implications for developers and web applications, and protect your own projects.
Quantum Computing Risks to Blockchain Explained
Dive into the growing quantum threat to blockchain security, exploring how quantum computers could break current cryptography and what Web3 projects can do to prepare now. Read more about protecting your assets.
Aave Bad Debt Crisis: The KelpDAO rsETH Exploit Explained
A $292M KelpDAO bridge exploit — enabled by a single-signer cross-chain mint with no multisig — left Aave with ~$200M in bad debt. Why threat modeling would have stopped it.
KelpDAO Exploit: Millions Lost to Liquid Restaking Attack
A massive $290M exploit targeting KelpDAO's rsETH liquid restaking protocol highlights critical vulnerabilities in DeFi. Learn how to secure your Web3 project.
Crypto Exchanges Under Attack: Grinex & Kraken Incidents Highlight Growing Insider Threats
Recent incidents involving Grinex and Kraken highlight a worrying trend: insider threats and geopolitical motivations targeting crypto exchanges. Learn how to bolster your exchange's security now.
Quantum Threat: Google Warns Ethereum at $100B Risk
Google's Quantum AI warns that five quantum attack paths could put over $100 billion in Ethereum assets at risk. Understand the future of blockchain security.
Claude Code Source Code Leaked via npm Source Maps: What You Need to Know
Anthropic's Claude Code CLI had its entire 512,000-line TypeScript codebase exposed through a misconfigured npm source map file. Here's what was revealed, how it happened, and the critical supply chain security lessons for every development team.
Cross-Chain Bridge Vulnerabilities and the DGLD Exploit
Dive into the critical vulnerabilities plaguing cross-chain bridges with the DGLD exploit. Learn how FYEO helps secure your Web3 projects. Read more!
Axios npm Package Compromised: Supply Chain Attack Deploys Cross-Platform RAT
Two malicious versions of the Axios npm package with 300M+ weekly downloads were published via a hijacked maintainer account, deploying a cross-platform Remote Access Trojan through a hidden dependency.
DeFi Governance Attacks: The Cheapest Exploit in Web3
Discover how governance attacks are costing DeFi protocols millions with minimal investment. Learn about the Moonwell incident and how to protect against web3 governance exploits. Read more.
Claude Code Security: What It Actually Is (And the Verification Problem Nobody's Talking About)
Last week Anthropic launched Claude Code Security and wiped $20B+ off cybersecurity stocks in two days. Having dug into the open-source code behind it, we think the real conversation is being missed.
FYEO completes a secure code assessment of Banger
FYEO completed a secure code assessment of Banger, an app for minting tweet collectibles, ensuring its security and integrity through ongoing audits.
FYEO performed a secure code assessment of the Theoriq Smart Contract
FYEO assessed the Theoriq smart contracts, a modular architecture for collective AI, facilitating secure agent registration, token operations, and proof anchoring.
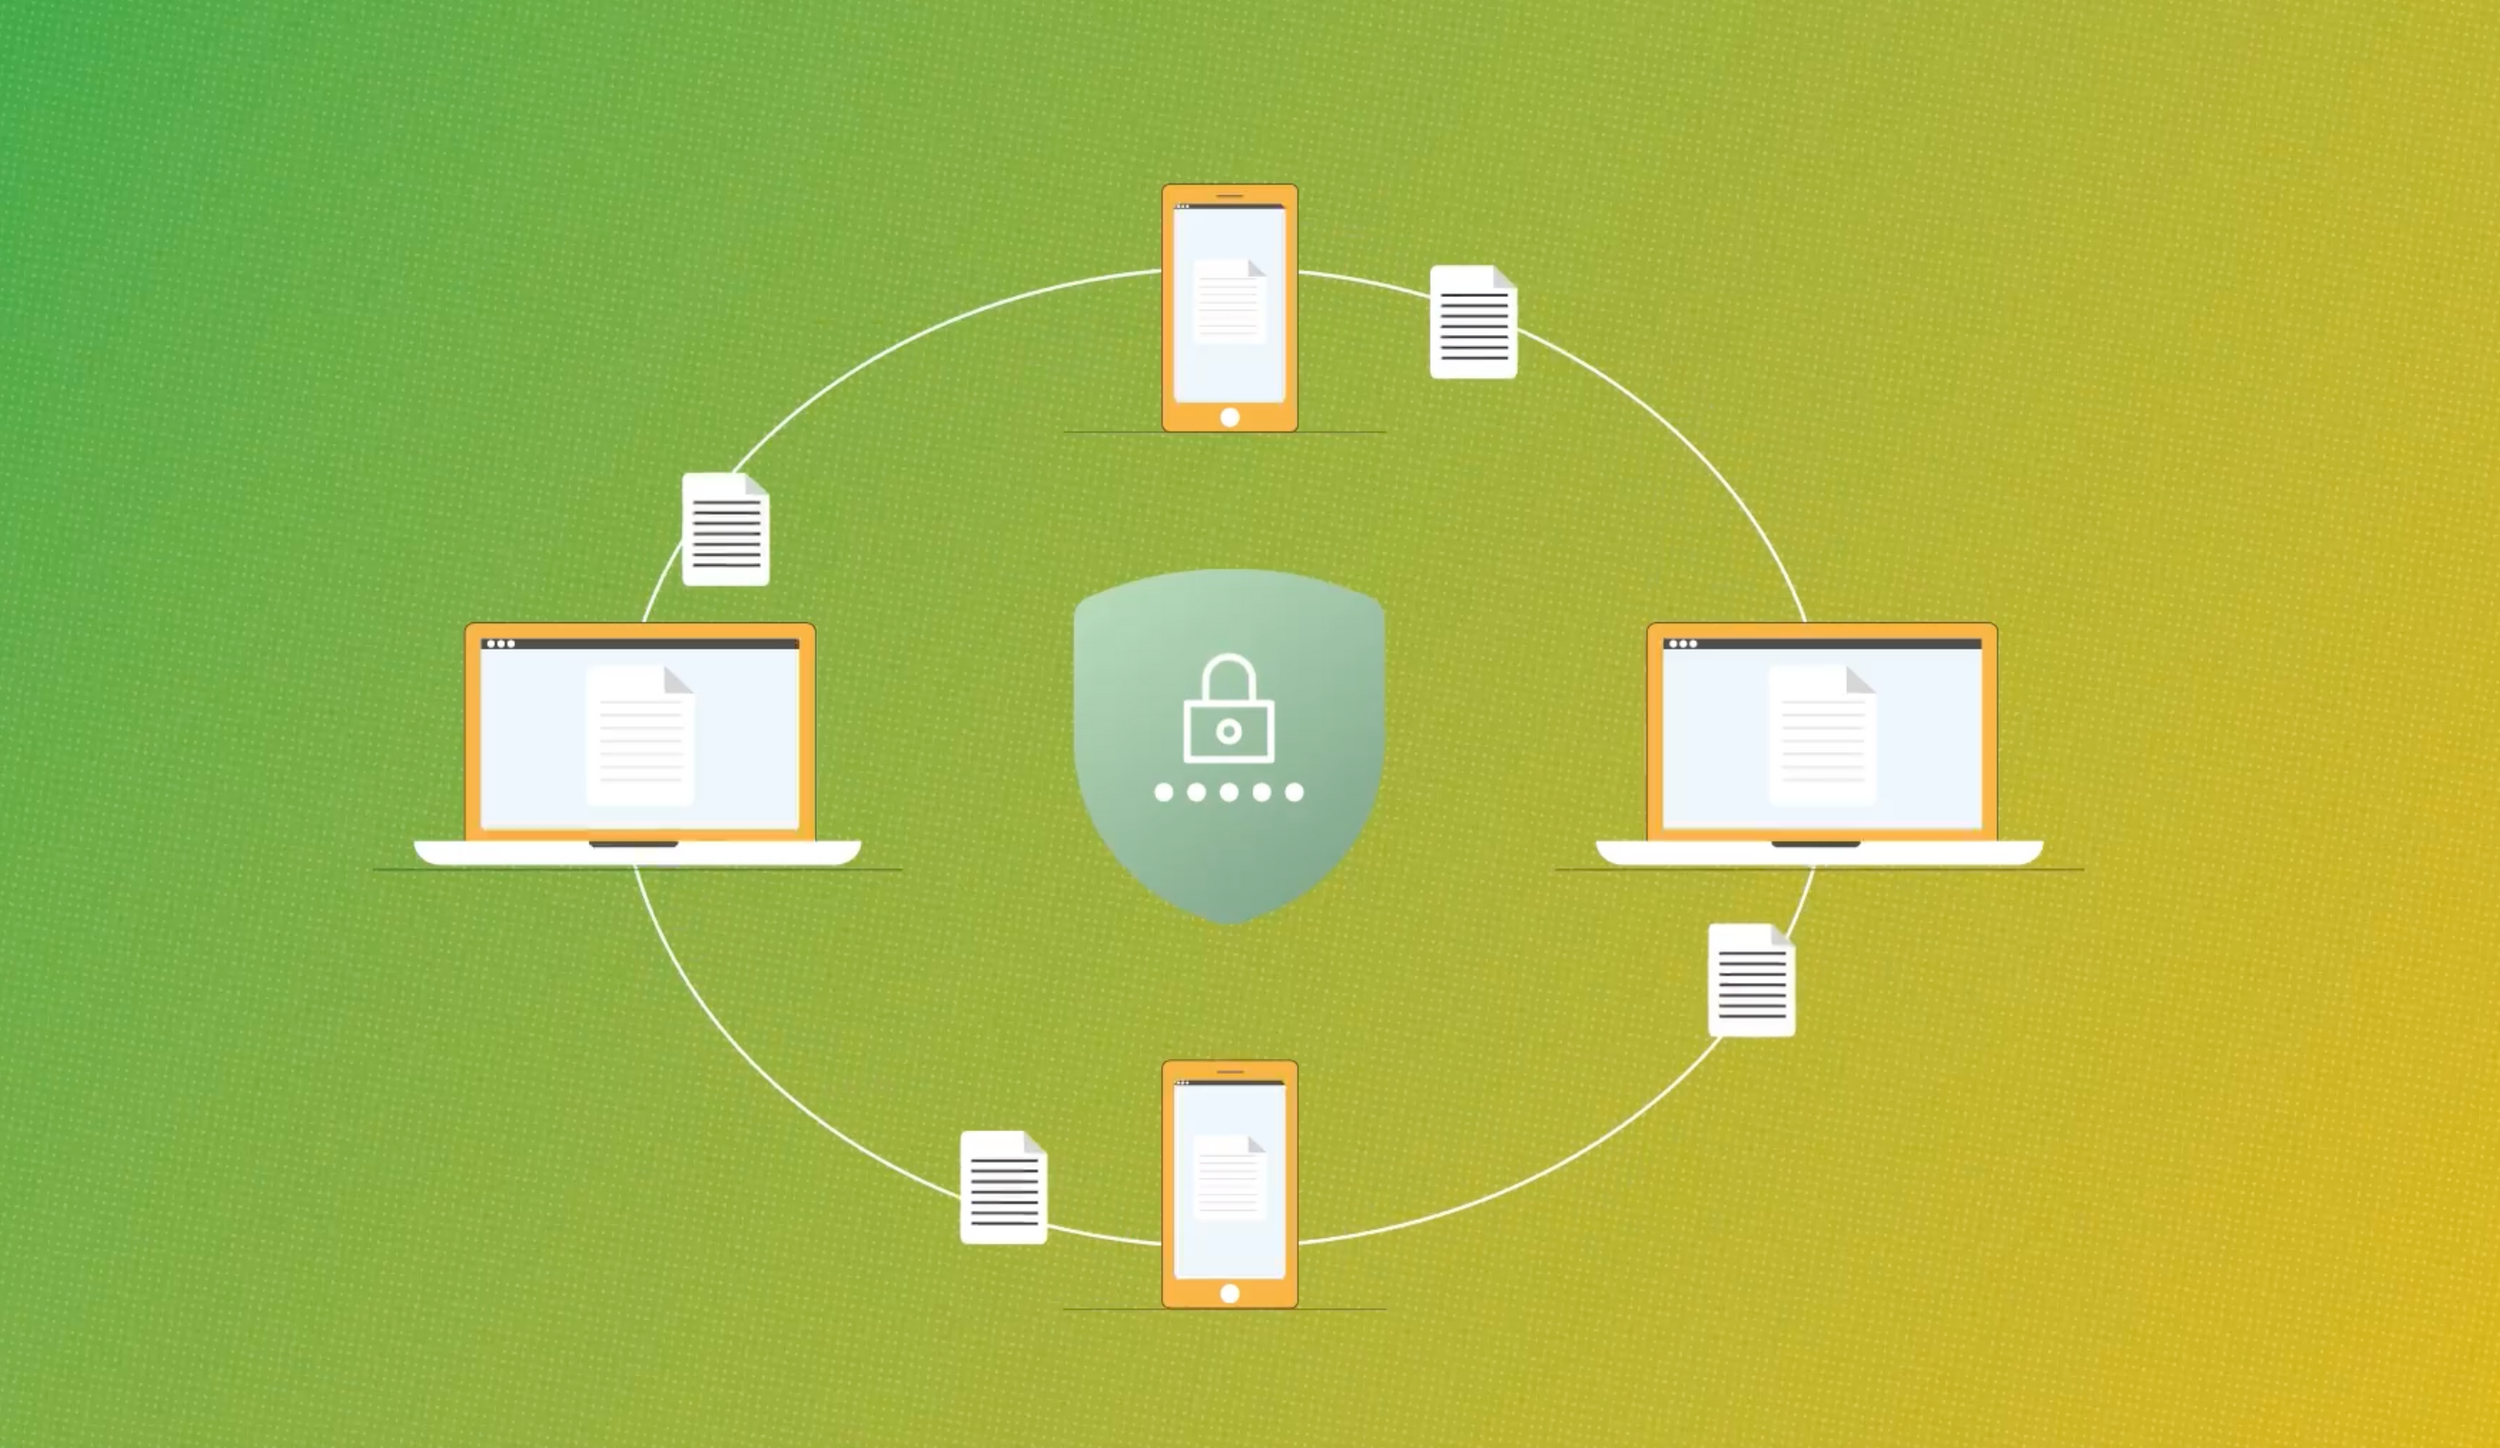
The Advantages of Peer-to-Peer Synchronization with KryptPass: A More Secure Approach to Data Management
KryptPass utilizes peer-to-peer synchronization for enhanced security and user control over data, offering a decentralized alternative to traditional password managers.
FYEO performed a secure code assessment of 4Cast Program
FYEO conducted a secure code assessment of the 4Cast Solana program, a decentralized prediction market. The review found 3 medium-severity, 1 low-severity, and 4 informational findings.
FYEO performs security assessment for identity.com
FYEO has performed security assessments for identity.com's Gateway Protocol EVM and did-bnb initiative, focusing on DID integration on EVM chains. All identified vulnerabilities were remediated.
FYEO & TruGard Partner to Enhance Web3 Security: Unveiling the Dangers of Smart Contract Honeypots
FYEO partnered with TruGard to highlight smart contract honeypot dangers in Web3. Manual verification by FYEO confirmed numerous honeypots detected by TruGard's AI analyst.
FYEO performed a secure code assessment of Flare Songbird
FYEO performed secure code assessments for Flare Songbird, including upgrades to Avalanche v1.10.0 and v1.9.0. All reviewed updates resulted in zero new security issues.
FYEO performed a secure code assessment of Aureus OX Oxen Flow application
FYEO assessed the Aureus Ox Oxen Flow iOS wallet application, which recently added XRPL functionality. The app is well-structured and uses secure practices for data storage and random number generation.
FYEO Completes Security Review of Evernode
FYEO completed a security review of Evernode's three Hooks, a Xahau-native project enabling decentralized applications on virtualized machines. Evernode addressed all issues to satisfaction.
KryptPass - Technical Overview of FYEO's Self-Custody Decentralized Password Manager
This technical overview details KryptPass, a patented, self-custody decentralized password manager using private-public key encryption for secure, user-controlled identity management.
FYEO performed a secure code assessment of 1INTRO
FYEO performed a secure code assessment of 1INTRO's 1DEX program on Solana. The review found a well-structured codebase with a commendable emphasis on security practices by the 1INTRO team.
FYEO performed a secure code assessment of the Samoyedcoin’s Saga Tools
FYEO conducted a secure code assessment of Samoyedcoin's Saga Tools, focusing on their Solana airdrop feature. The Samo team promptly remediated identified findings.
FYEO performed a secure code assessment of Drift Token
FYEO performed a security audit of the $DRIFT token smart contract for GameFi studio DRIFT Labs prior to its token generation event. Minor errors were identified and addressed by the team.
Cybersecurity Trends February 2024: Threat Intelligence Report
February 2024 saw 17 incidents compromising over 55.9M records, including a French healthcare breach. Mac malware targeting crypto enthusiasts also emerged.
Cybersecurity Trends January 2024: Threat Intelligence Report
January 2024 featured malware-infested ads and LockBit's ransomware attack on Subway. 17 incidents led to over 71.9M records being compromised.
FYEO Completes Security Review of Censo
FYEO completed a secure code review of the Censo iOS and Android applications, a seed phrase manager designed to protect crypto assets. Findings were reported for both platforms.
Cybercrime - Trends Overview & 2024 Forecast
Cybercrime grew 40% annually since 2020, impacting the global economy. Social engineering and compromised credentials drive attacks, with growth projected to reach +19% in 2024.
Cybersecurity Trends November 2023: Threat Intelligence Report
November 2023 saw new revelations in the Okta breach, rise of 'identity wallets', and significant increases in phishing and malware domains. Over 16M records were compromised.
Cybersecurity Trends October 2023: Threat Intelligence Report
October 2023 highlighted the Okta breach and new Android malware. Phishing and malware domains rose significantly, with over 16.9M records compromised in various incidents.
FYEO Completes Security Review of Xahaud - Codebase for Xahau
FYEO completed a security review of Xahaud, the codebase for the Xahau network. All identified vulnerabilities were remediated by the XRPL Labs team.
Reel in Your Security with Cryptophishies: The Phish Who’s Making a Splash in Web3!
FYEO launches Cryptophishies NFTs, featuring an AI anti-phishing mascot named Fisko. NFT holders get early access to FYEO's phishing protection Chrome extension.
Cybersecurity Trends September 2023: Threat Intelligence Report
September 2023 was dominated by massive ransomware attacks on MGM and Caesars. Phishing and malware activity continued, with over 15.1M records compromised.
Cybersecurity Trends August 2023: Threat Intelligence Report
August 2023 trends included exploitation of Ivanti vulnerabilities and .us domain phishing. A significant data breach at Forever 21 compromised over 500k individuals.
Interview with Brian Gale, FYEO Co-CEO
FYEO Co-CEO Brian Gale discusses the company's cybersecurity approach in Web2 and Web3, including AI streamlining audits and a decentralized identity solution.
Cybersecurity Trends July 2023: Threat Intelligence Report
July 2023 saw a spike in PDF malware and a fabricated Microsoft crypto wallet site. The Tigo platform data leak exposed over 700,000 users' personal data.
FYEO Completes Bifrost Wallet Security Assessment
Towo Labs engaged FYEO to perform a secure code review of the Bifrost Wallet, a secure and private self-custody crypto wallet for 10+ blockchains.
Cybersecurity Trends May 2023: Threat Intelligence Report
May 2023 saw a rise in phishing and malware domains, with over 721 similar domains and 12K malware domains identified. Data breaches compromised 98M records.
Cybersecurity Trends April 2023: Threat Intelligence Report
April 2023 reported 681K new domains, 3.3K phishing, and 14K malware domains. Over 4M records were compromised in 120+ data breaches.
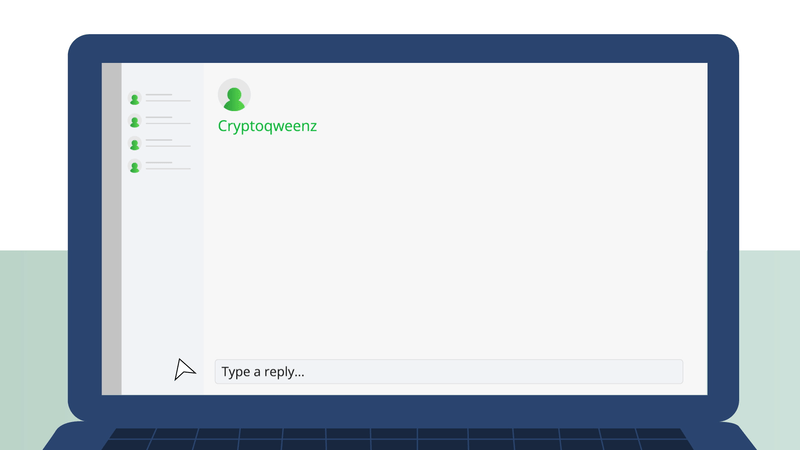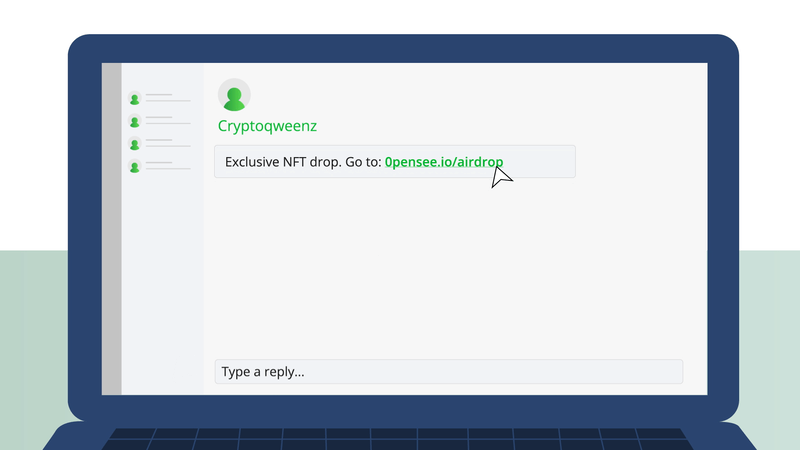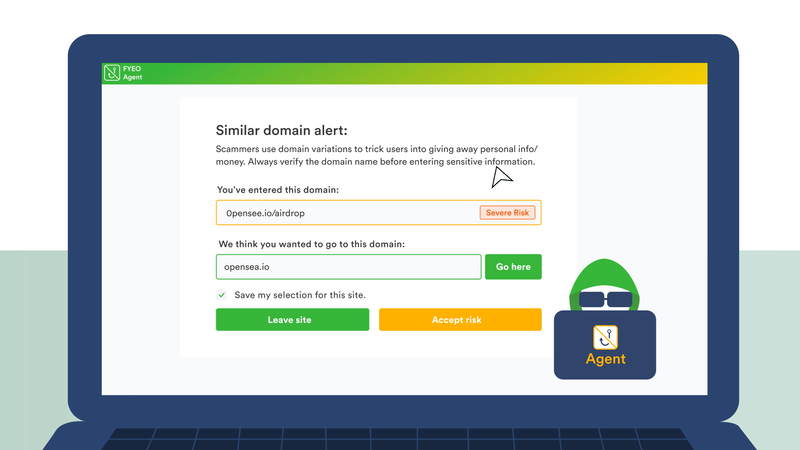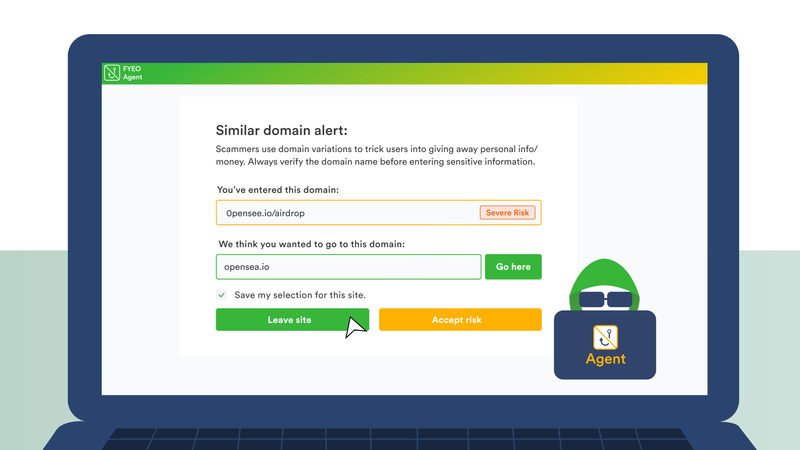
FYEO Agent: An Evolutionary Approach to Phishing Protection
FYEO Agent offers advanced, real-time phishing protection via a browser extension using AI and a dynamic site reputation database.
Cybersecurity Trends March 2023
March 2023 saw 8.9M new domains, 3.9K phishing, and 1.4K malware domains. Over 41.9M records were compromised across 100+ data breaches.
Ransomware Group Deep Dive: BlackCat
BlackCat, also known as ALPHV, is a ransomware-as-a-service group that uses double extortion tactics. They demand millions in ransoms and threaten to leak victim data if payment isn't made.